Hackers Spending in Ad Accounts They Broke Into
Half a million dollars stolen from ad accounts in three days. Here's how the hackers are getting in, what they do once they have access, and the specific Meta settings every advertiser should lock down right now.

Over half a million dollars stolen in 3 days
Hackers spending in ad accounts they broke into.
I've heard several stories like this and a brand I work with was recently attacked
I've been working on FB ads for 14 years and this is the worst I've seen.
Let's dig into how they're doing it, how to prevent this from happening to you, what to do if it does, and what Meta needs to fix/change to prevent this from continuing.
If you don't read this, don't come crying to me when it happens to you!
These attackers are somehow getting access to the business and granting ad account access to their own businesses.
(I believe they're doing this through FB apps and the API, more on that later)
The attackers created campaigns and ad sets that mimicked the ones already in the account, making them very difficult to spot immediately.
The ads were driving from their pages to their URLs, but this is hard to spot if you're not looking for it.
By the time you notice, it's too late, they've maxed out budgets.
They used active ad accounts and old dormant ad accounts that nobody paid attention to but still had active payment sources.
Some of you reading this could even be running trojan horse ads in your accounts right now and not even notice it.
If someone changed the page and URL of *1* ad in your account, how long would it take you to notice?
These attackers drove to ads for things like 'lose weight quick' gummies and were probably just stealing (gullible) users' credit card info.
There are conversions for the ads because they shared their pixels to the ad accounts so they could optimize the ads to their events.
There's no trace of the partners being added in Business Manager history (likely through the API)
This is a huge security issue (or bug) that Meta needs to fix.

(You can find the Business History in your Business Info page)
Business Manager has become a huge tangled rats nest of access and logic that requires years of trial and error to fully understand.
A user can advertise with a page they have access to from Business A in the ad account from Business B, but Business B can't prevent that.
Hackers have gotten pretty advanced and seem to be using Facebook apps to get access and grant their businesses access.
One compromised admin user can sneakily allow partners access to spend thousands or take down an entire business.
Here's an example of the access an app can have of your business and ad accounts:
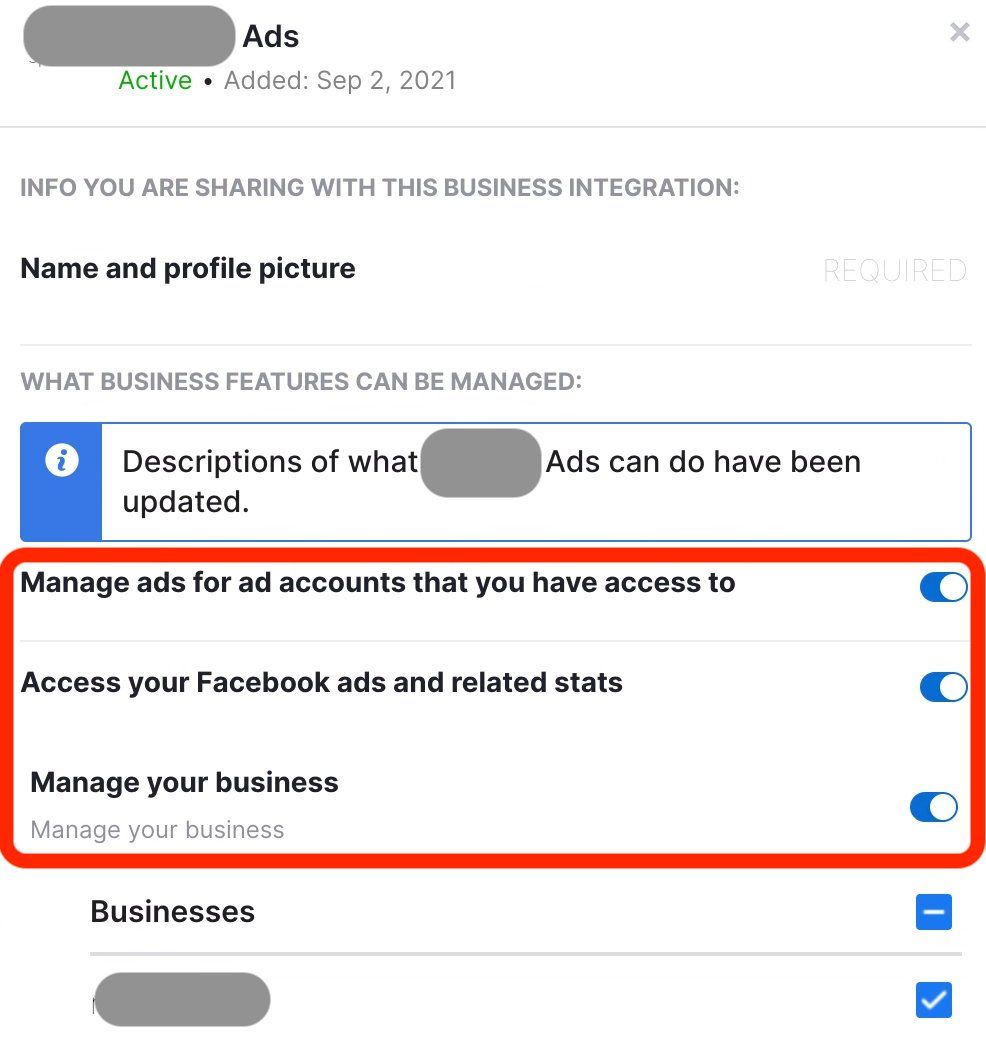
Good news: A business integration's access to your personal information automatically expires after 90 days of inactivity.
TERRIFYING NEWS: this expired access does not affect a business integration's connection to your business assets and information.

This means these apps can continue to access your business in perpetuity and other admins can't see what apps have access to the business.
Sure there are good uses for this (apps like Sprinklr or SproutSocial), but this also creates a dangerous situation for bad actors.
Technically, a hacker can develop a Facebook app (or acquire/steal an existing app) that users can approve to give access to their business settings.
The businesses have no way to see or block access to what apps can access their assets if they wanted.
Example:
Another admin of my business manager clicks a malicious/spoofed link and approves access to a malicious app.
That app now has complete access to my business and can grant access to my ad accounts to other businesses through the API.
Nothing I can do to stop it.
Meta needs to address these security issues and make Business Manager more secure from malicious apps and users.
This can affect any size business or agency.
The bigger your available funding source/credit limit, the bigger the risk.
Here are some steps to secure your business:
Make sure your BM requires 2 factor authentication. DO IT.
Ask your admins to review their personal Business Integration settings for any old/unrecognized apps:
https://www.facebook.com/settings?tab=business_tools&ref=settings
Be vigilant about new admins and partners!
If you find your account(s) were compromised:
Immediately pause your campaigns and reduce/cap any increased budgets.
Contact Facebook support and summarize the situation and what was lost as best you can.
Remove unknown partners and admins
Meta *should* hopefully refund you
I chatted with Tod Maffin about how this topic as well as other Meta business security concerns on his podcast here.
Also on YouTube here.


